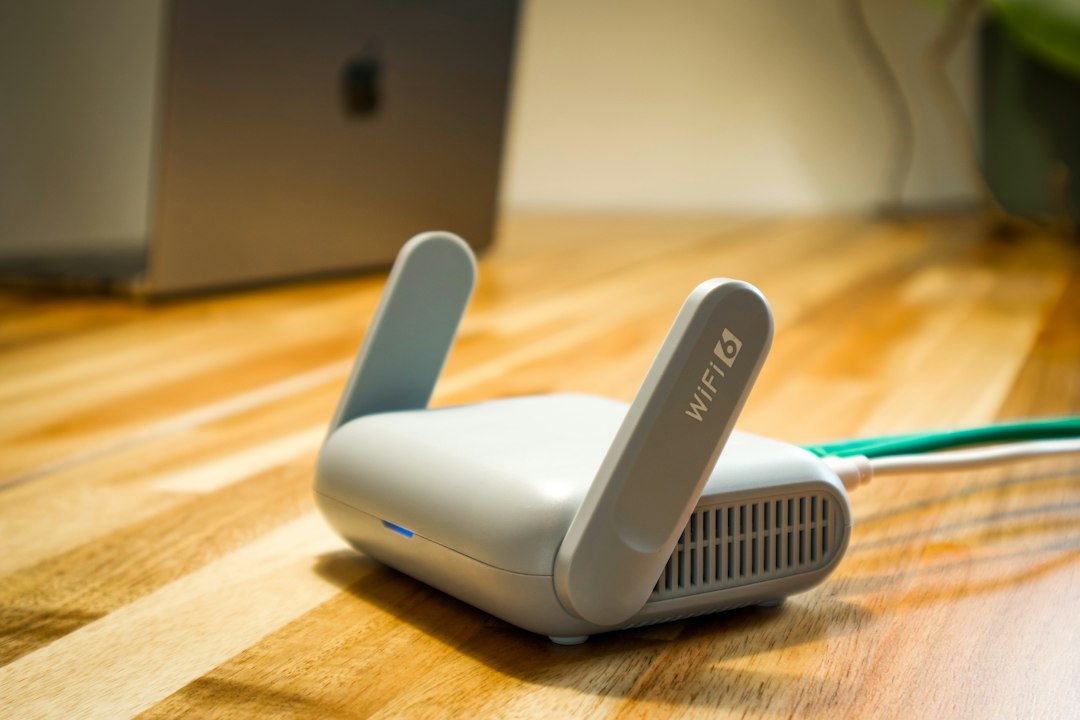
Five US states are now suing TP-Link, the company behind the most common home and small-office routers in America. The cases turn on TP-Link router security claims and on how far the firm has really separated itself from China. None of it has been proven in court. So if a TP-Link box sits at the edge of your office or your staff’s homes, the story is worth ten minutes of your time.
Table of Contents
What the states say about TP-Link router security
Texas sued first, in February 2026. Florida, Iowa, Montana and Nebraska filed on 6 October. The complaints are consumer-protection cases, so the argument is about what TP-Link told buyers, not about a proven backdoor.
The states say the company oversold its security and overstated its distance from China. Nebraska’s attorney general also says TP-Link’s supply chain remains tied to China’s state-backed technology sector. Its Vietnam plant, he says, gets most of its components from or through China.
The next day Nebraska’s Mike Hilgers led a coalition of 21 attorneys general in a letter to the FCC. It concerns TP-Link’s request for conditional approval to sell new router models. The state reports that TP-Link holds at least 60% of the US retail market for Wi-Fi systems and small-office routers.
TP-Link’s answer
TP-Link calls the suits “built on false premises”. In a statement dated 6 October, it says it has given regulators records showing its US-sold devices are made in Vietnam and that it is independent of any foreign government. It also says it will not share customer network data with foreign governments or unauthorised third parties.
A court will settle that dispute. You can act on TP-Link router security without picking a side.
A separate set of flaws landed the same week
The lawsuits and a batch of new vulnerabilities are not linked, and neither the complaints nor the advisories connect them. But the timing is useful, because the flaws show what a router weakness looks like in practice.
TP-Link published an advisory covering five CVEs, CVE-2025-30237 to CVE-2025-30241, in its Aginet range of ISP-managed mesh systems, routers, PON units and DSL modems. SEC Consult, which found the bugs in December 2024, published its own write-up on 8 October. It says the flaws together let an attacker on the same network fully compromise a device.
- CVE-2025-30237 is an authentication bypass in the web server (CVSS 4.0 score 8.7).
- CVE-2025-30238 lets a low-privileged user create an admin account and switch on SSH (8.6).
- CVE-2025-30239 comes from hardcoded keys that protect stored configuration (8.5).
- CVE-2025-30241 allows OS command injection as root (8.6).
There is no workaround. Fixes depend on the ISP, and TP-Link warns that firmware for ISP versions may not be available for direct download. Neither advisory reports exploitation.
What this means for a UK business
Most UK readers will not be buying these exact units. But the lesson travels. A router is the one device that every other device trusts, and it is often the least managed box in the building.
First, start with an inventory. List every router, modem and mesh unit across your sites, including the ones staff use for home working, and note the make, model and firmware version. Cannot answer that in an afternoon? That is your first finding.
Next, check support dates for each model. The lawsuits cite the Archer AX21, which TP-Link says reached end of life in May 2024. Old hardware is a standing risk, whatever the brand.
Then look at who controls updates, because that decides how fast you can patch. Where an ISP manages the device, you may be waiting on them for patches. Ask for the firmware version and the patch policy in writing.
Finally, test the edge. A network penetration test will show whether a management interface is exposed, whether default or weak credentials are in use, and whether a compromised router could reach your internal systems. We have seen the same pattern in other cases, such as the ASUS router hack and a MikroTik compromise check.
Why TP-Link router security is a process, not a brand
Some firms will be tempted to swap one vendor for another and call the job done. That treats geopolitics as a security control. Every router maker has shipped serious bugs, and every one of them ends up with unsupported models in the field.
A better approach is boring. Know what you run, patch it on a schedule, retire what is unsupported, and have someone test it from the outside. If you want help scoping that for your own sites, get in touch with Aardwolf Security.
Why “who made it” is the wrong question
Good TP-Link router security does not depend on the verdict. Politics will dominate the coverage of these cases. For a security team, the useful question is simpler: what can an attacker do with this device, and how fast would we know? Nebraska says attackers have gained administrator access to routers and enlisted them into botnets. Once that happens, the router can be used to reach other systems or to move data out quietly.
Because of that, logging matters. Many small-business routers keep almost no useful logs, and most owners never read them. If yours can forward logs to a central place, turn that on. If it cannot, treat it as a reason to upgrade at the next refresh.
Subscribe to our newsletter
Honest updates, straight to your inbox. Unsubscribe any time.